Do you keep seeing Amplifyapp.com on your device? If yes, you should take it seriously. Detections like this are often linked to potentially unwanted programs (PUPs), seqüestradores de navegador, or unsafe domains that can expose you to scam pages, phishing attempts, e malware downloads.
Many users ignore this kind of warning because the device still appears to work. But that is exactly how PUP-related threats stay active — they run in the background, change browser settings, push ads, and redirect traffic while looking like a minor annoyance instead of a real security issue, similar to PUP browser redirect behavior.
Neste artigo, you will learn what Amplifyapp.com may represent, how PUPs and browser hijackers behave, why repeated redirects are dangerous, and why recurring scam or ad pages can be a sign of malware on your computer.
What Is Amplifyapp.com?
Amplifyapp.com is commonly associated with a programa potencialmente indesejado (PUP), browser redirect alerts, or an unsafe domain event. A PUP is not always classified as a traditional virus, but it can still create serious problems for your device, privacidade, and browsing security, as seen in unwanted software cases.
These programs are often distributed through bundled installers, misleading ads, fake updates, and low-quality download websites. Microsoft specifically treats potentially unwanted apps as a risk category because they can negatively affect device performance, user control, e segurança.
In many cases, a detection like Amplifyapp.com appears when a redirect-related threat is active:
- A suspicious app or browser component has been installed.
- Your browser is being redirected to unsafe or deceptive domains.
- An ad-supported program is injecting ads or sponsored links.
- A browser hijacker has modified your default search or homepage.
- A scam-related site keeps reappearing due to hidden software on the system.
Even if the software looks harmless at first, the long-term risk comes from what it enables: tracking, phishing exposure, scam redirects, and sometimes malware delivery.
| Nome ameaça | Amplifyapp.com |
| Tipo |
Browser Redirect Alerts, PUP, Unsafe Domain |
| Risk Level | Medium to High (Tracking, redirecionamentos, Scam Exposure, Possible Malware Delivery) |
| Common Symptoms | redirecionamentos, pop-ups, changed homepage/search, intrusive ads, suspicious domains, slower browsing |
| Detecção + Remoção |
Mais informações sobre SpyHunter e guia de desinstalação. Antes de proceder, consulte SpyHunter de EULA e Critérios de avaliação da ameaça. A Política de Privacidade do SpyHunter pode ser encontrado na após ligação. Tenha em mente que scanner de SpyHunter é totalmente gratuito. If the software detects a threat, you can remove it via the available options in the product. |
What Does Amplifyapp.com Do?
Threats in this category are usually built for one or more of these goals: ad revenue, traffic redirection, data collection, and user manipulation. Even if the software is not classified as a destructive virus, it can still cause security problems by repeatedly exposing you to scam websites and untrusted downloads, como redirect/adware detections.

In practical terms, Amplifyapp.com may behave like an ad-supported browser hijacker or unsafe redirect component. It often affects the browsing experience first, then gradually creates privacy and security risks over time, similar to browser hijacker infections.
1) Browser Setting Changes
One of the most common effects of a PUP or hijacker is unauthorized browser modification. The software may change settings in ways commonly seen with search redirect hijackers:
- Your default search engine
- Your homepage
- Your new tab behavior
- Browser shortcut targets
- Installed extensions or add-ons
These changes are not just annoying. They allow the program to control where your traffic goes, which increases the chances of seeing ads, Links patrocinados, e scam pages.
2) Redirects to Suspicious or Scam Domains
Amplifyapp.com may cause redirects to questionable websites, fake search engines, or pages designed to trick users into clicking “Allow,” downloading software, or entering personal details, similar to redirect-to-scam domains.
Security agencies and consumer protection organizations repeatedly warn that scam and phishing pages often use urgency, spoofed branding, and deceptive links to steal information or install malicious files. FTC and CISA guidance specifically highlights suspicious links, urgent messages, and malicious attachments as common scam tactics.
If your browser is opening unsafe pages by itself, that is a strong signal that the issue is not just “one bad website” — it may be a browser hijacker, adware app, or another hidden component causing the redirects, as in persistent browser redirects.
3) Intrusive Ads and Sponsored Content Injection
Ad-supported PUPs are designed to monetize your browsing. Once active, they may inject banners, pop-ups, em anúncios de texto, cupons, or sponsored links into pages you visit. Some even replace legitimate search results with paid or deceptive results, a pattern seen in ads virus cases.
This behavior creates multiple risks, Incluindo fake ad redirects:
- You may click a fake ad that looks like a normal site link.
- You may be sent to scam stores or phishing pages.
- You may trigger downloads of more unwanted software.
- You may see misleading “system alerts” or fake warnings.
Em outras palavras, the PUP is not only displaying ads — it is increasing your exposure to online fraud and malware campaigns, much like fake antivirus scam ecosystems.
4) Tracking and Data Collection
Many browser hijackers and PUPs use tracking technology to monitor browsing behavior, which is commonly reported in online safety guides. This may include:
- Search queries
- Visited pages
- Clicked links and ads
- Browser type and device details
- IP address or geolocation-related data
Some threats also try to collect form entries, endereço de e-mail, usernames, or other identifiers. The collected data can then be shared with third parties or used to deliver more targeted (and often more convincing) scam content, as with traffic-manipulating threats.
This is why “just adware” can still become a real privacy issue. The software may be profiling your activity and using that data to push more dangerous pages over time, similar to unsafe domain detections.
Why It May Be a Sign of Malware on Your Computer
A lot of users see a detection like Amplifyapp.com and assume it is simply a weird website. Sometimes that is true. But if the same unsafe domain or redirect keeps returning, there is a strong chance your device has a deeper issue, as seen in recurring scam-domain cases.
Repeated redirect behavior often points to one of the following, Incluindo notification-spam abuse:
1) A Hidden PUP Installed with Another Program
Potentially unwanted apps are frequently bundled with freeware installers or fake updates. Microsoft’s documentation on PUA/PUP protection reflects this risk category because these apps can alter user experience and security settings without clear consent.
E se Amplifyapp.com started appearing after installing a free app, codec, converter, or browser extension, that is a common infection path for adware and hijackers, similar to bundled unwanted apps.
2) A Malicious or Unwanted Browser Extension
Some extensions appear useful but secretly inject ads, redirect searches, or collect browsing data. Users often install them from pop-ups, fake update pages, or aggressive ads. Once active, the extension may keep sending you to unsafe domains until it is fully removed, as with malicious browser add-ons.
This is especially common when scam pages ask users to “enable notifications,” “add extension,” or “allow access” before viewing content, a tactic used by deceptive prompt pages.
3) Browser Notification Abuse
Scam pages frequently trick users into clicking “Allow” on browser notification prompts. Depois disso, spam notifications can continue to appear long after the original site is closed, pushing fake alerts, prizes, crypto scams, and malware-laced ads, similar to scare-pop-up campaigns.
Many victims think their whole PC is infected when they see these pop-ups, but the root problem is often a combination of notification abuse plus an adware/PUP component that first drove them to the scam site, as described in scam redirect cleanup guides.
4) Trojan or Loader Activity Triggering Redirects
In more serious cases, redirect behavior may be caused by a Trojan, downloader, or malware loader running in the background. These threats can alter traffic flow, open browser sessions, or drop additional adware and hijacker components, similar to Trojan loader activity.
If the redirects are frequent, aggressive, or paired with other symptoms (slowdowns, unknown processes, security warnings, disabled settings), you should treat the situation as a possible malware infection and not just a browser annoyance, as in heuristic malware detections.
What Are the Dangers of Leaving It Active?
The biggest risk of ignoring Amplifyapp.com is that PUPs and unsafe-domain redirects usually get worse over time. They often start with ads and slow browsing, but can gradually increase your exposure to scams and malware, much like brand-impersonation scam redirects.
Here are the most common consequences, Incluindo phishing-based account theft:
- Account theft: Redirects can lead to fake login pages that steal passwords and verification codes. FTC and FBI both warn that spoofed/phishing websites are designed to collect credentials and financial data.
- Financial fraud: Users may be redirected to fake payment, compras, or banking pages.
- Privacy loss: Tracking components can collect browsing patterns and personal details.
- More malware: Unsafe ads and fake updates can install additional threats.
- System instability: PUPs often consume resources and interfere with normal browsing.
Even if you avoid clicking the ads, the constant redirect behavior itself is a red flag. It usually means your browser or system is no longer fully under your control, similar to persistent hijacker-style behavior.
Why a Professional Anti-Malware Scan Is Recommended
Se você está vendo Amplifyapp.com repeatedly, a full anti-malware scan is usually the fastest and safest way to determine whether the problem is limited to a PUP or part of a larger malware issue, as with Trojan-related cleanup.
A trusted anti-malware scanner can help identify hidden malicious components:
- Adware and PUP components
- Browser hijackers and redirect modules
- Malicious or unwanted extensions
- Startup entries and hidden persistence files
- Additional malware installed alongside the PUP
Microsoft also emphasizes keeping devices updated and using security protections to reduce exposure to unwanted software and malicious downloads.
If the detection keeps returning after you close the browser or restart the computer, that is usually a sign the underlying component is still active. A proper system scan helps uncover those hidden parts and reduces the chance of reinfection, similar to multi-component infections.
Run a Free Scan for Amplifyapp.com
Final Thoughts on Amplifyapp.com
Amplifyapp.com is commonly linked to a potentially unwanted program, browser hijacker behavior, or unsafe domain redirects. While these threats may not always look like traditional viruses, they can still create serious problems by exposing users to scams, phishing pages, tracking, and further malware downloads, as seen in active malware campaigns.
The most important thing is not to ignore repeated redirects, suspicious ads, or browser changes. Those are often early warning signs that your system or browser has already been altered, much like other compromise indicators.
If you suspect your device is affected, run a reputable anti-malware scan as soon as possible to check for hidden components and restore control of your browser and system security with a trusted scanner.
Preparation before removal of Amplifyapp.com:
1.Certifique-se de fazer backup de seus arquivos.
2.Certifique-se de ter esta página de instruções sempre aberta para que você pode seguir os passos.
3.Seja paciente como a remoção pode demorar algum tempo.
Passo 1: Reinicie o computador no Modo de Segurança:
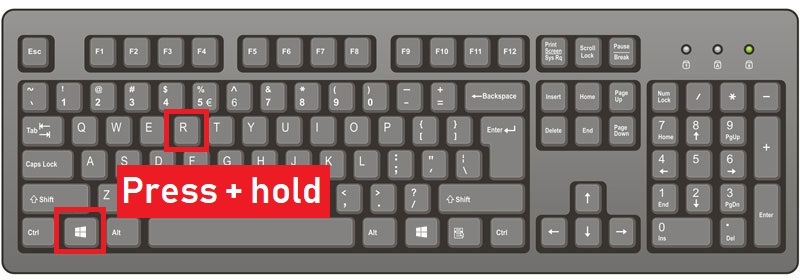
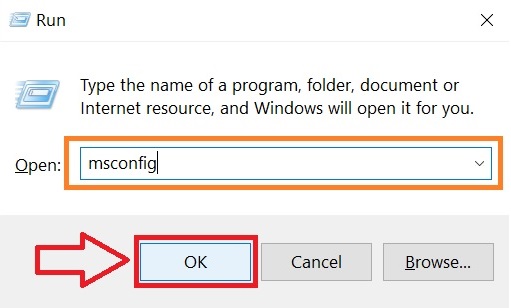
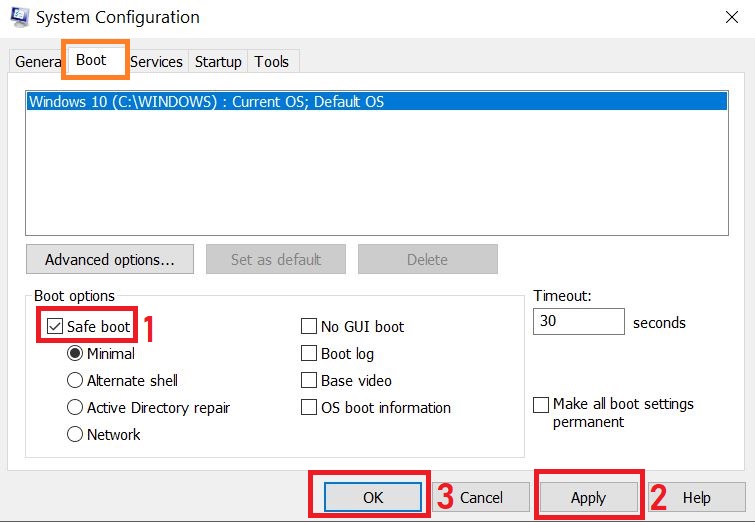
Passo 2: Cut out Amplifyapp.com in Task Manager
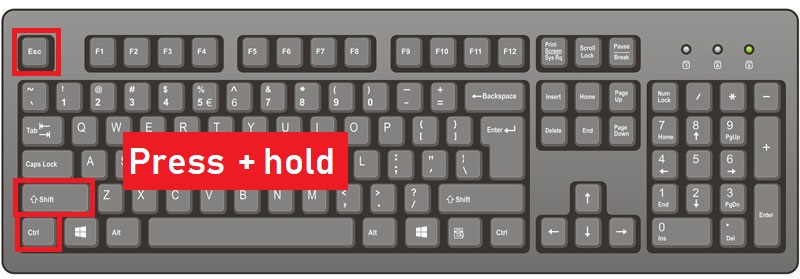
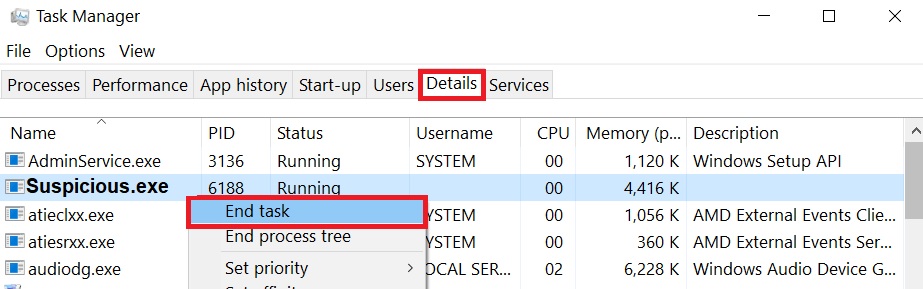
Passo 3: Eliminate Amplifyapp.com‘s Malicious Registries.
Para a maioria das variantes do Windows:
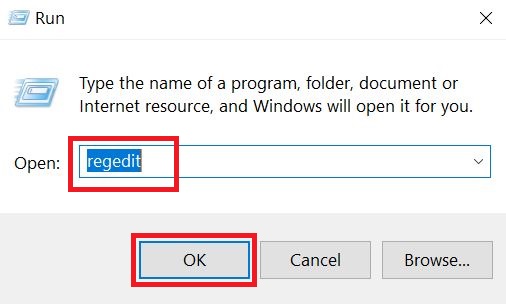
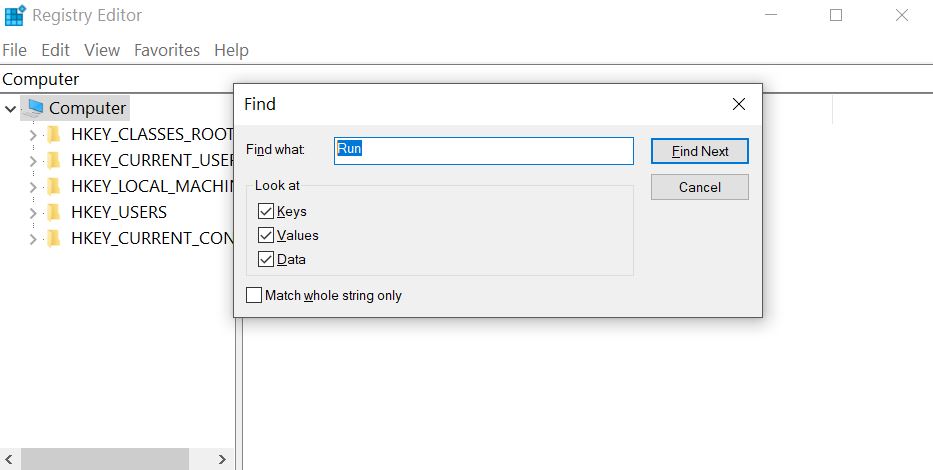
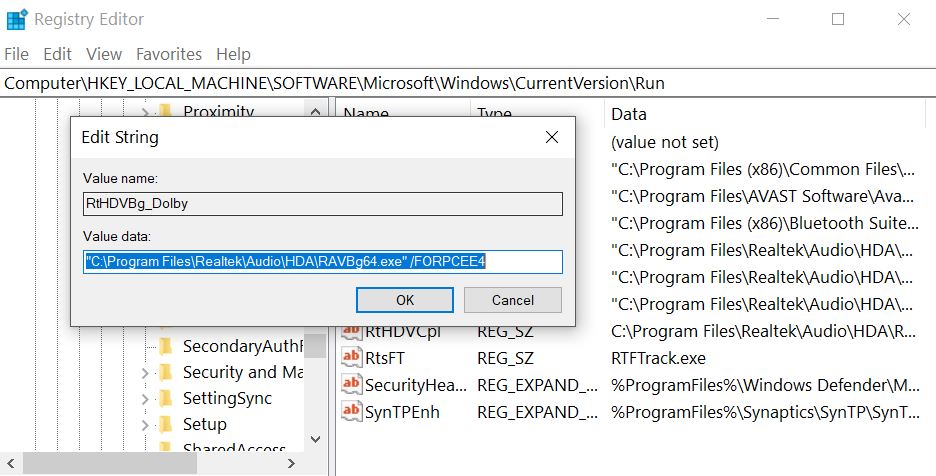
Passo 4: Digitalizar para todos os arquivos de vírus, related to Amplifyapp.com and secure your system.
Se você estiver em Modo de segurança, inicializar novamente no modo normal e siga os passos abaixo
É aconselhável executar uma varredura livre antes de cometer a versão completa. Você deve se certificar de que o malware é detectado pelo SpyHunter primeiro.